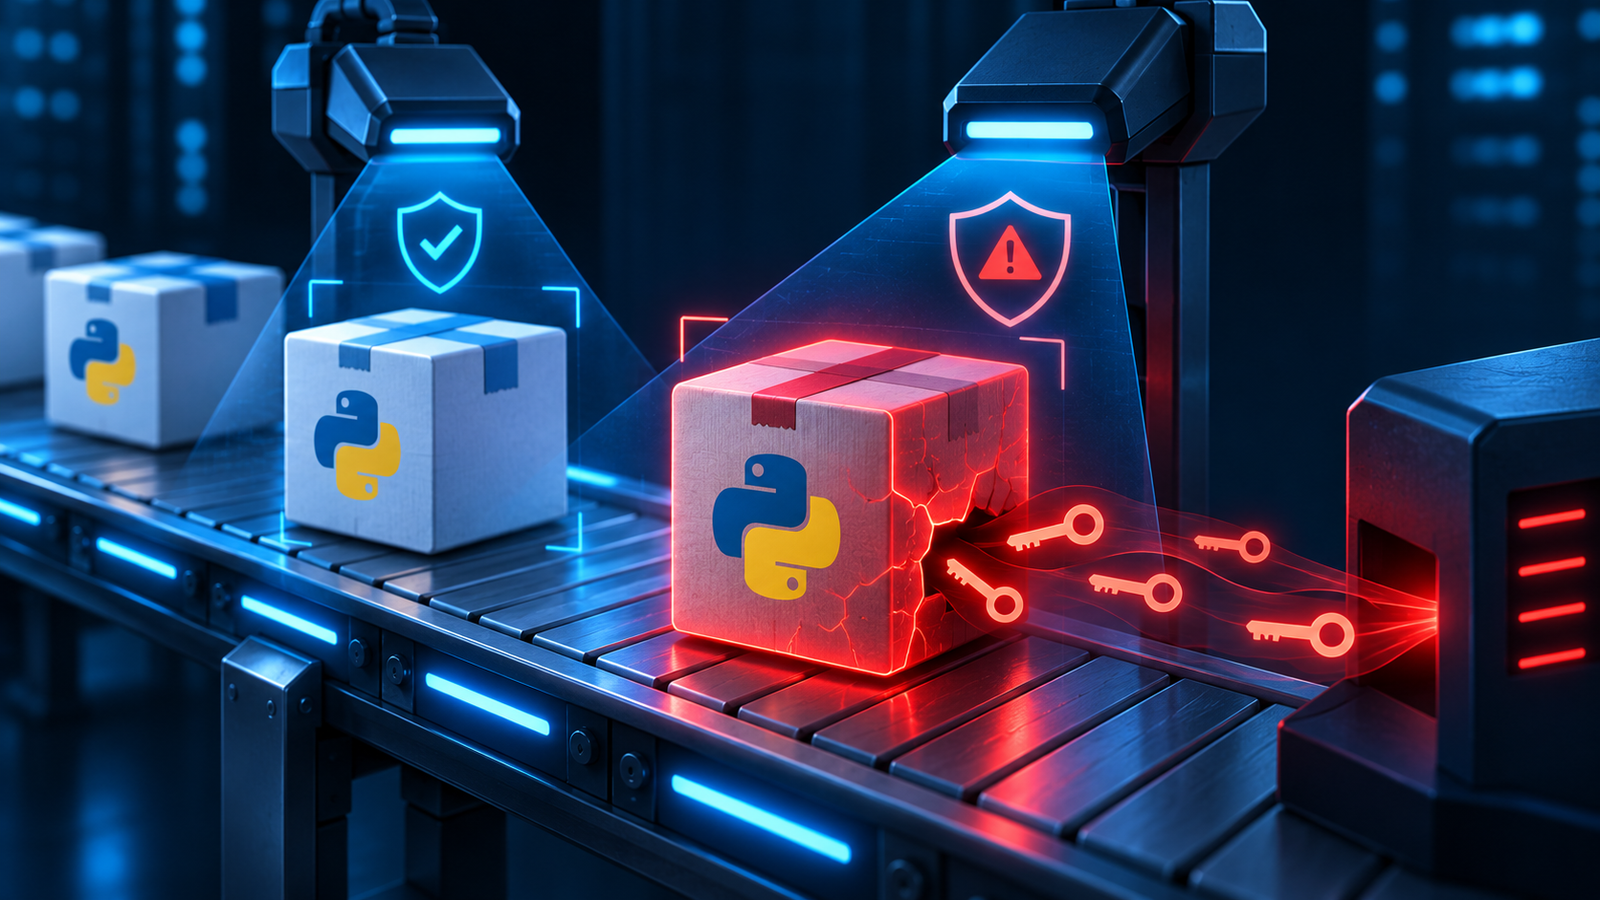
Two malicious Microsoft Agent Framework releases were published to PyPI on November 17. Versions 1.26.1 and 1.26.2 carried a credential stealer that could run whenever Python started, even if the library was never imported by an application.
What happened
Elastic Security Labs says it detected the activity roughly six minutes after publication. Analyses from Elastic, StepSecurity and SecurityWeek found that the malicious packages used a .pth startup hook. Python processes automatically load these files, making the incident more dangerous than a library that must first be imported.
What data was targeted?
The malware searched for tokens and credentials tied to cloud platforms, developer tools and continuous-integration pipelines. Such secrets can provide access to repositories, package registries and connected systems.
Recommended response
- Search endpoints, containers, caches and CI logs for versions 1.26.1 and 1.26.2.
- Remove affected environments and rebuild them from a trusted source.
- Revoke and rotate every secret that was accessible from those environments.
- Review logs for unusual authentication or package-publishing activity.
- Pin dependencies and add provenance checks to build pipelines.
Installing a compromised package does not by itself prove that a stolen secret was later used, but it should be treated as potential exposure. Public reporting has not yet conclusively established how the publishing process was compromised.